Skip to content
Menu

If an adversary gets a foothold in your corporate network today, can they reach operations?  

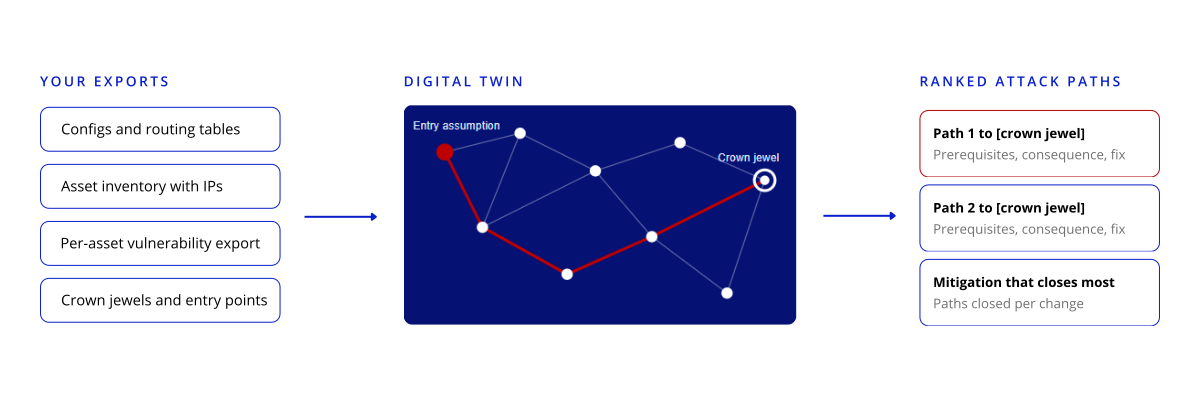
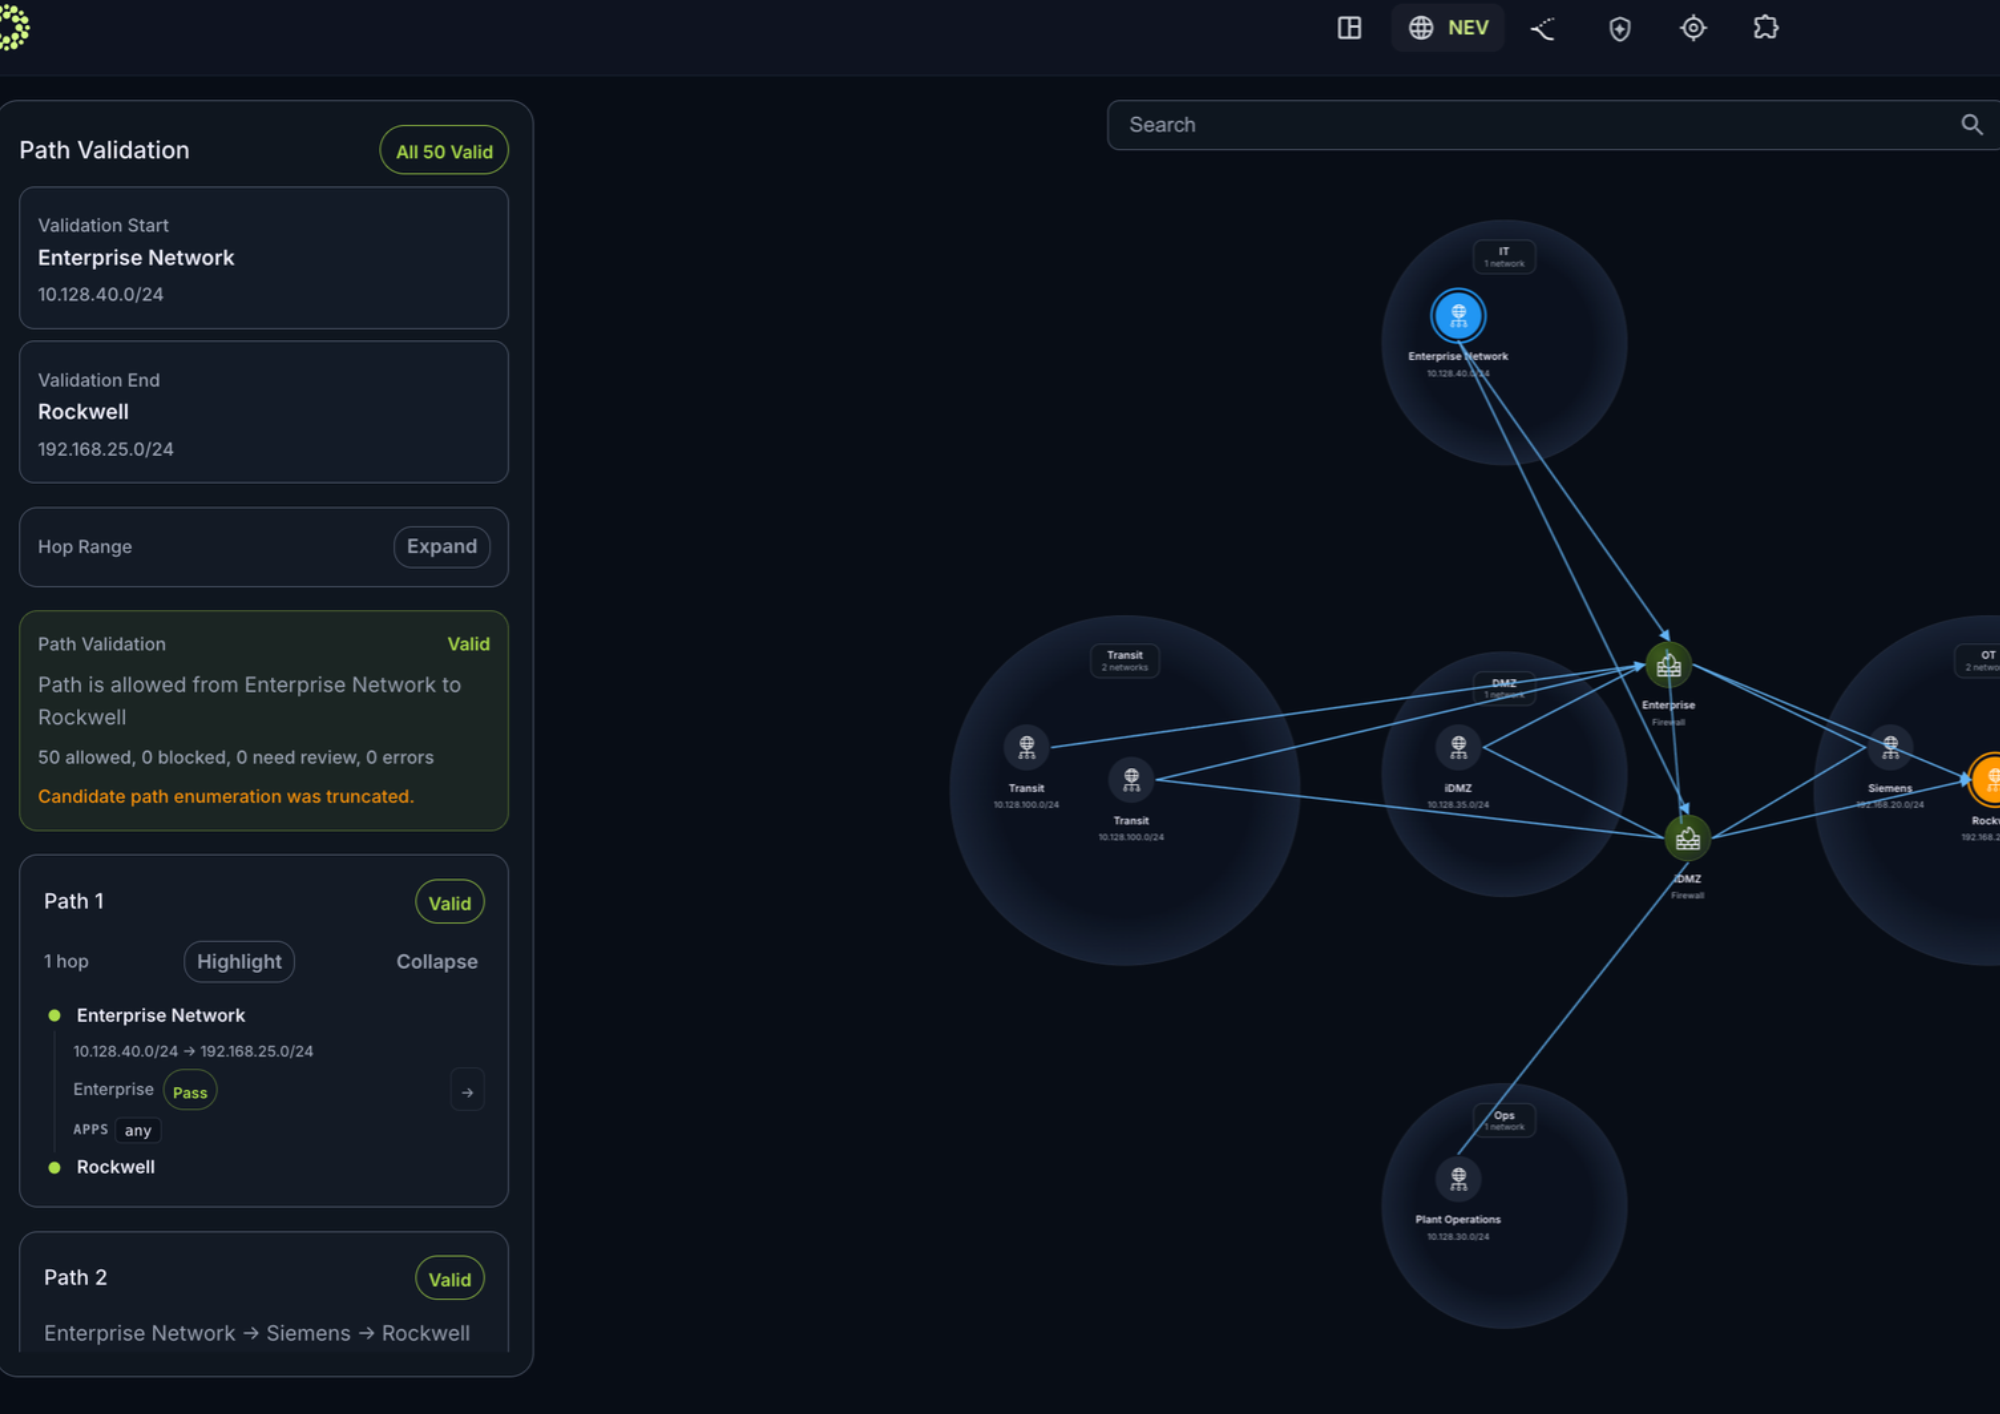
TSG/ControlBurn transforms live OT configurations into a digital twin to simulate breach paths, reveal where attackers can get through and what they can reach, and prioritize the risks that matter most. Delivered by TSG and powered by platform partner, Frenos.


Your OT assessment has a half-life

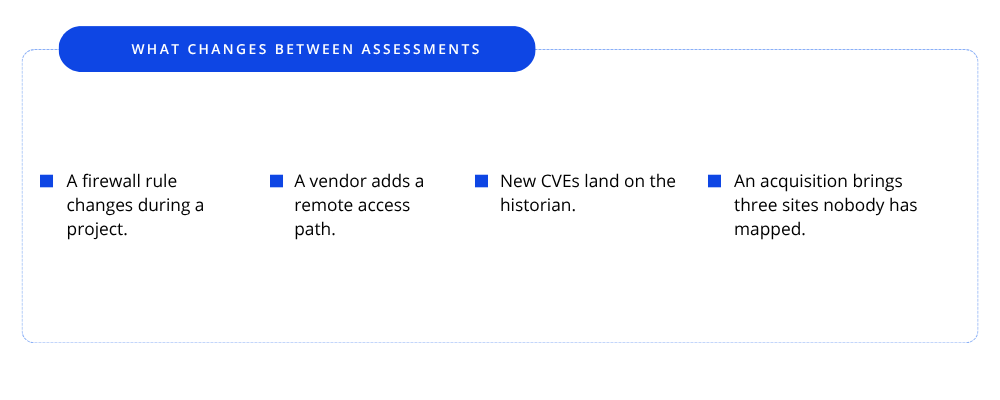
The moment an OT assessment is complete, it starts aging. A firewall change, new asset, vendor access, or emerging vulnerability can create an attack path that didn’t exist when the environment was assessed.

WHAT CHANGES BETWEEN ASSESSMENTS
 

ENTERPRISE FRICTION

What changed for the attacker

Testing more is the right instinct and the wrong mechanism. 

The skill floor dropped

AI-assisted adversaries compress the correlation work that used to gate an OT intrusion: configs against inventories against CVE lists. Attack paths that once needed a specialist are within reach of less capable actors.

Manual testing does not scale

Manual OT penetration testing does not come down in cost or up in frequency. Safety constraints limit what a tester can touch, outage windows limit when, and the pool of qualified testers limits how often. 

 OUR OPERATING SYSTEM
 

How TSG/ControlBurn works

Steps 1-3 are powered by the platform. Steps 4 and 5 require consulting expertise, and that’s where most reports usually die. 

technology icon (5)

PLATFORM (FRENOS)
Ingest
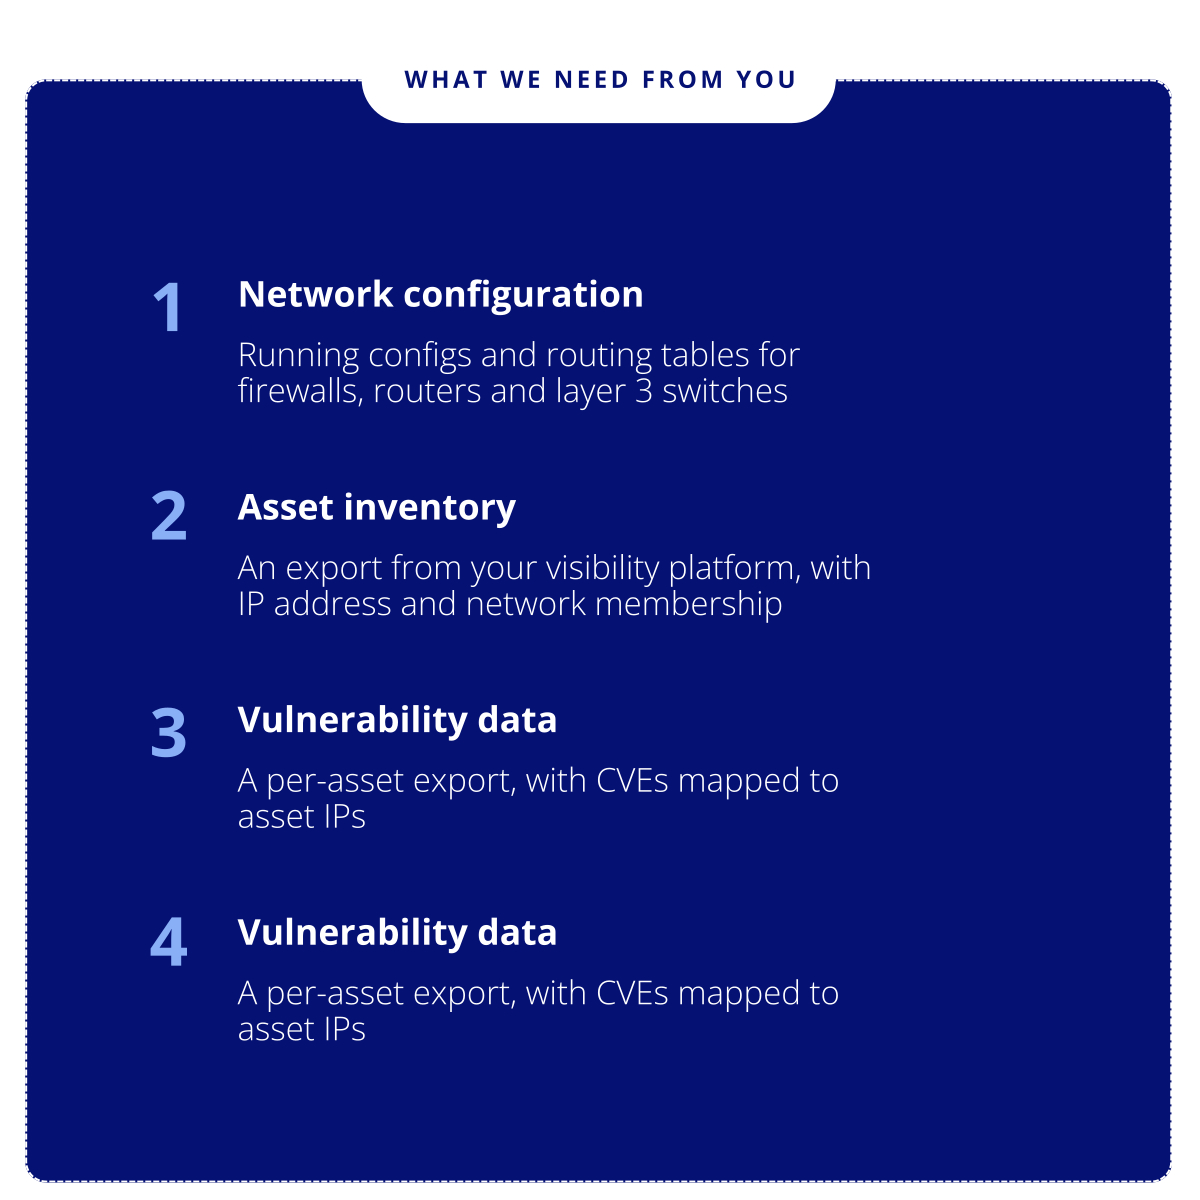
Firewall and router configs, routing tables, asset inventory, vulnerability exports. Data you already collect. 

02 icon

PLATFORM (FRENOS)
Model
A digital twin of your environment, built from those exports rather than from the live network. 

02 icon (1)

PLATFORM (FRENOS)
Simulate
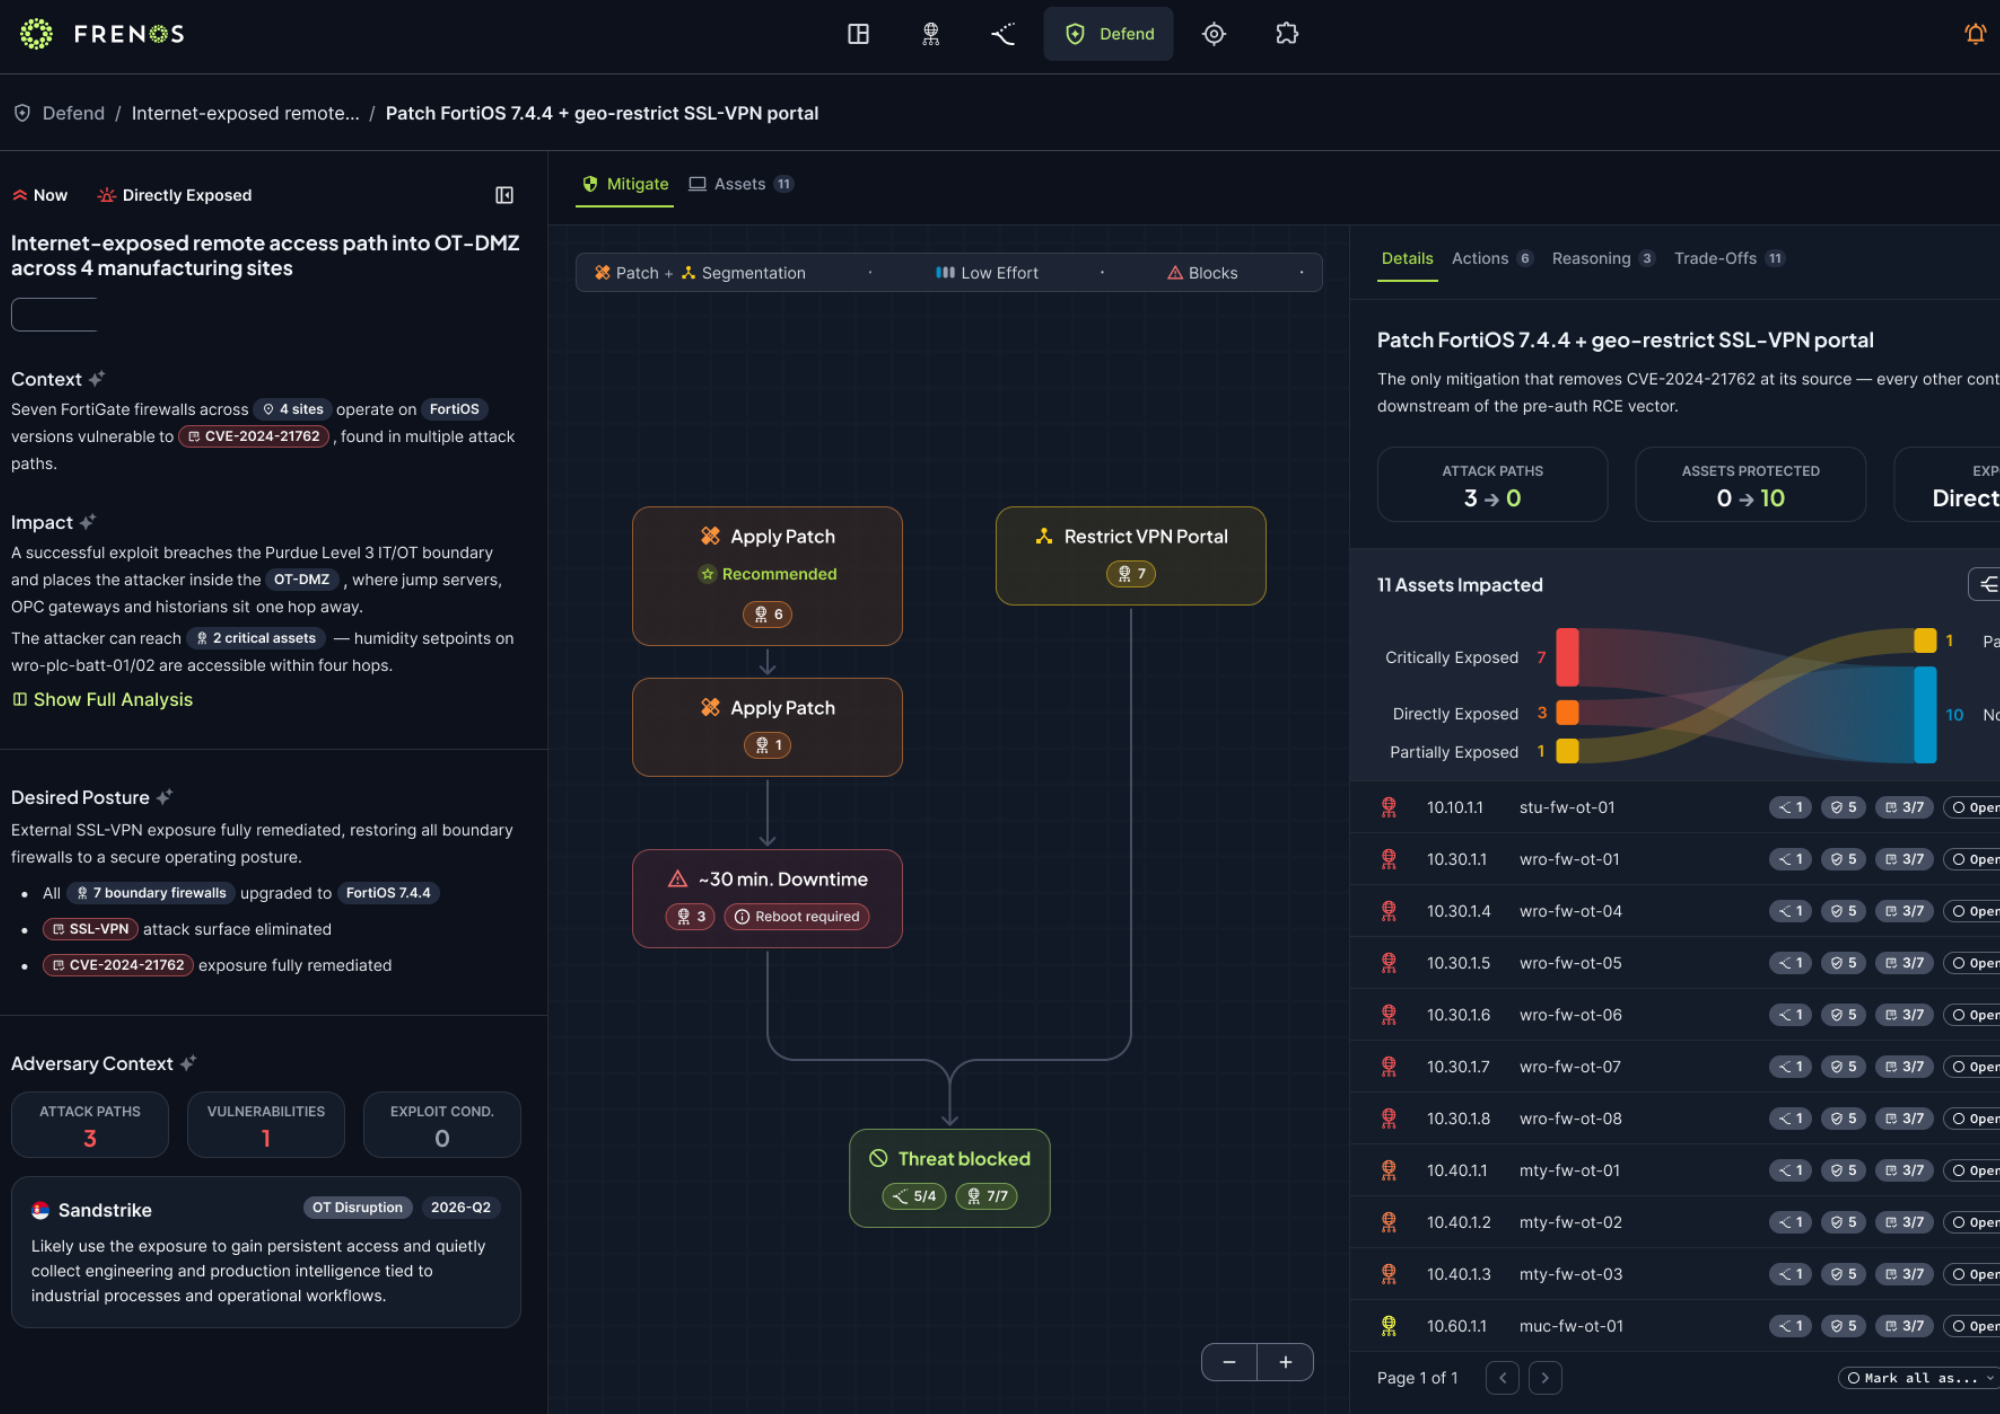
Adversary simulations against the twin, ranking the paths that reach the assets you name as critical. 

04 icon

THE SELECT GROUP
Act
We select the mitigations that fit your operation, ranked by paths closed. You leave with a roadmap, and in Advisory and Implementation we help package, prove and make the changes. 

05 icon

THE SELECT GROUP
Validate
After each change, the simulation re-runs on refreshed configurations to prove the path is gone, not moved. 
 OUR expertise
 

What the platform proves and what never happens

DIGITAL TWIN (1)
What the platform proves
  • Segmentation validated against your configurations, not your diagrams
  • Attack paths ranked by whether they reach the assets you name as critical
  • Vulnerability triage by reachability against the modeled paths, with exploitability confirmed jointly with your engineers
  • Blast radius for the zones in scope


Nothing touches production

Frenos platform needs no agents, no scanning and no production access, and that every simulated attack runs inside the twin rather than the live network.

Deployment is available on premises or fully air-gapped. Deployment is available on premises or fully air-gapped. Deployment is available on 


ENGAGEMENT MODELS

Three tiers. One starting point.

Every tier starts with the same four-day Foundation engagement. The tiers differ in what TSG does after the readout. 

Untitled design (3)
Four days. One site.

Interviews, twin build, simulation and a live readout. You leave with ranked attack paths, a mitigation set and a roadmap, and your team executes it.

What it settles: where an adversary can reach, and what to fix first.  


Tier 2 consulting
Foundation, then advice through the roadmap.

We prioritize the backlog by paths closed and by what is safe in a live process, package each change for your change board, and re-validate after every change. Your engineers make every change. 

What it settles: which fixes come first, and proof that each one worked. 
 

Tier 3
Consulting, plus hands on the changes.

The Select Group engineers make approved changes alongside your engineers, following your change control processes and outage windows. 

What it settles: getting approved changes made when your team cannot get them through.
What you can measure

 
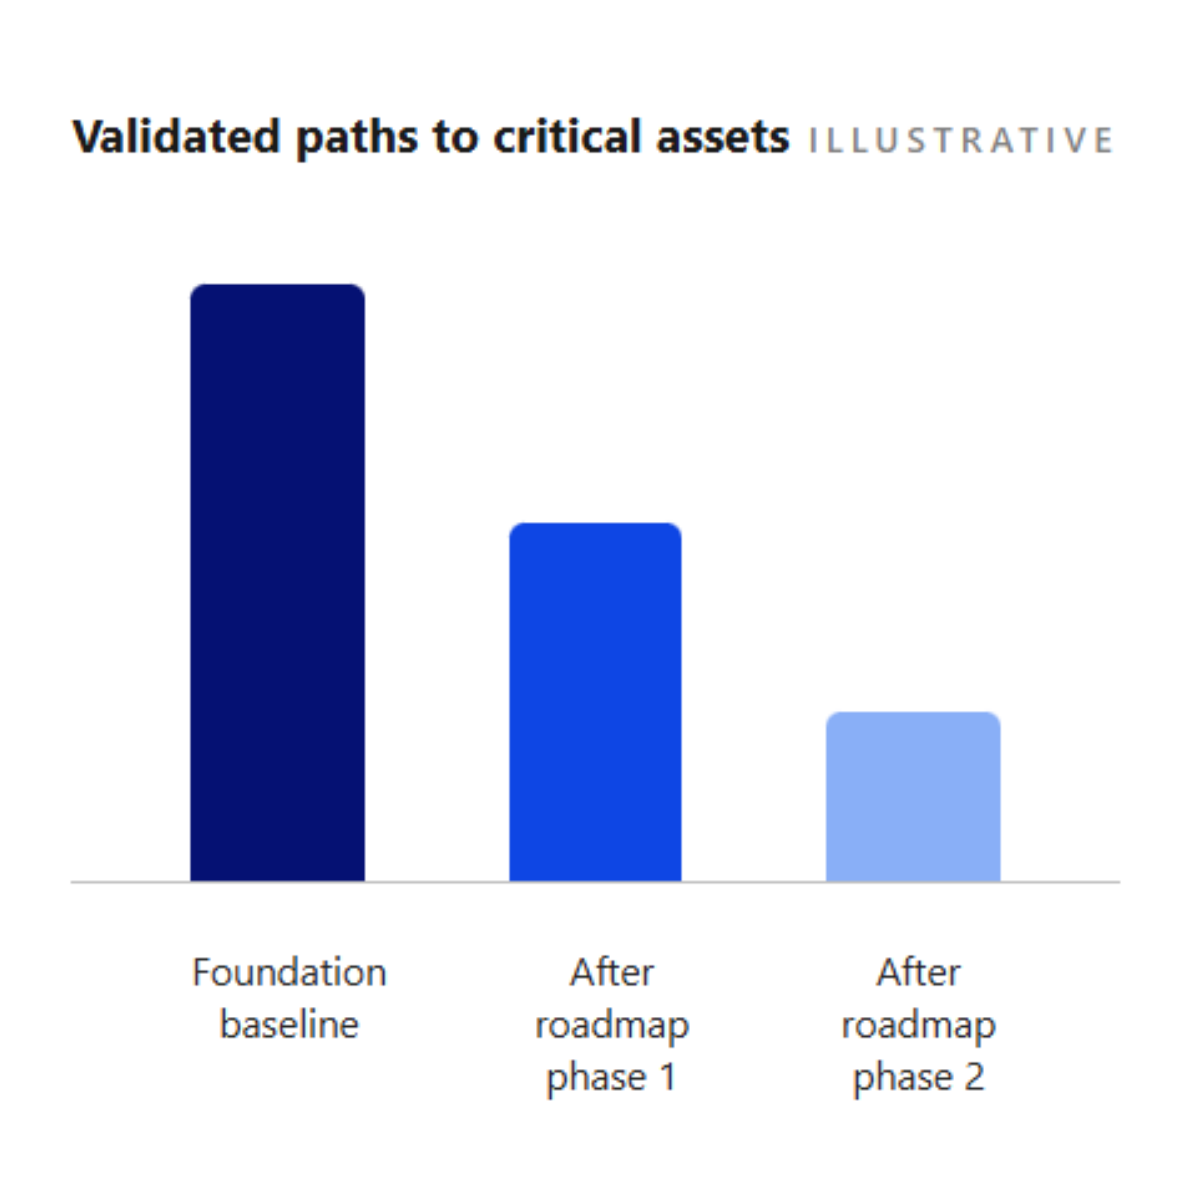
  • Validated attack paths to your named critical assets, before and after each roadmap phase 
  • Paths closed per change implemented 
  • Vulnerabilities reachable on a modeled path, against the total reported 
  • In Advisory and Implementation, time from finding to validated closure 
Digital twins blog post (1)
 

CLIENTS WE SERVE

Built for environments that can't afford to go down

The service is for every industry TSG serves: Communications, Consumer and Industrials, Energy and Utilities, Federal Services, Financial Services, Healthcare and Life Sciences, and Technology. Any environment with networked operational systems and a physical consequence of compromise is in scope, which now includes building management systems, data center facilities infrastructure, clinical device networks, and production lines.

communications industry
Communications
 
Central offices, mobile switching centers, headend and hub sites, and OSS/BSS environments spread across large, distributed footprints. Understand exposure across the estate.  


utilities industry
Energy and utilities
 
Generation, transmission, distribution, SCADA, and DCS environments where a cyberattack can become an operational event. Validate pathways between corporate IT and critical OT systems. 
industrials industry
Consumer and industrials
 

Production lines, manufacturing systems, and plant environments that change with every modernization initiative. Validate exposure before and after major infrastructure changes. 

federal services industry
Federal services
 
Mission and installation control systems, including highly restricted and disconnected environments. Assess exposure without requiring internet connectivity. 
 
financial services
Financial services
 
Data center facilities and building management systems that can sit outside traditional application-security programs. Validate pathways between facilities infrastructure and corporate networks. 
Hover Service Cards
Healthcare and life sciences
 
Clinical device networks and operational systems where uptime and strict change control are non-negotiable. Start by validating segmentation between clinical and enterprise environments. 
Untitled design (81)
Technology
 

Data center facilities, hardware manufacturing environments, labs, and the operational infrastructure behind the product. Identify potential pathways across lab, manufacturing, facilities, and corporate networks. 

Digital twins blog post (1)-1

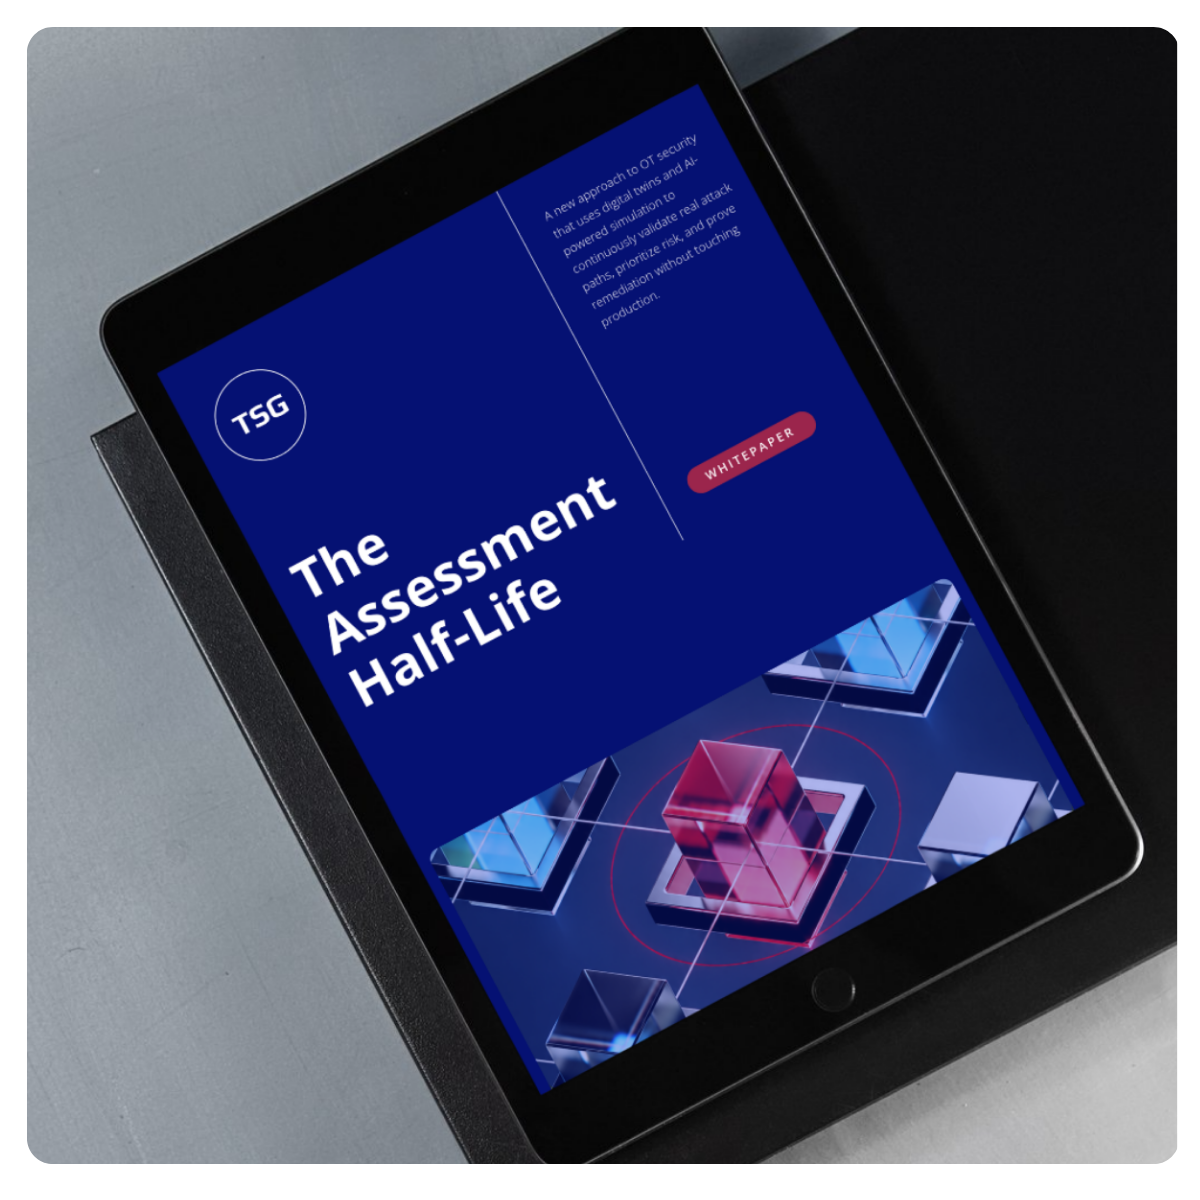
WHITEPAPER


The assessment half-life

A new approach to OT security that uses digital twins and AI-powered simulation to continuously validate real attack paths, prioritize risk, and prove remediation without touching production. 

WHY TSG

Trust built beyond the technology 


Technology can expose the attack path. Reducing the risk requires operational context, trusted data, and the ability to drive remediation. Frenos provides the technology to model the environment and expose viable attack paths. TSG brings the data, operational expertise, and execution needed to turn that intelligence into action. Together, we turn attack-path intelligence into prioritized action that reduces real-world risk. 


Untitled Design (6)

We do the unglamorous

A twin is only as accurate as the configuration exports feeding it. We chase the exports, check their dates, and tell you what the data cannot support before the readout, not during it. 
Untitled Design (7)

We work inside operations

In Advisory and Implementation, an OT/ICS advisor reviews every mitigation that touches a process or safety system. Changes go through your change board and your outage windows, not around them. 
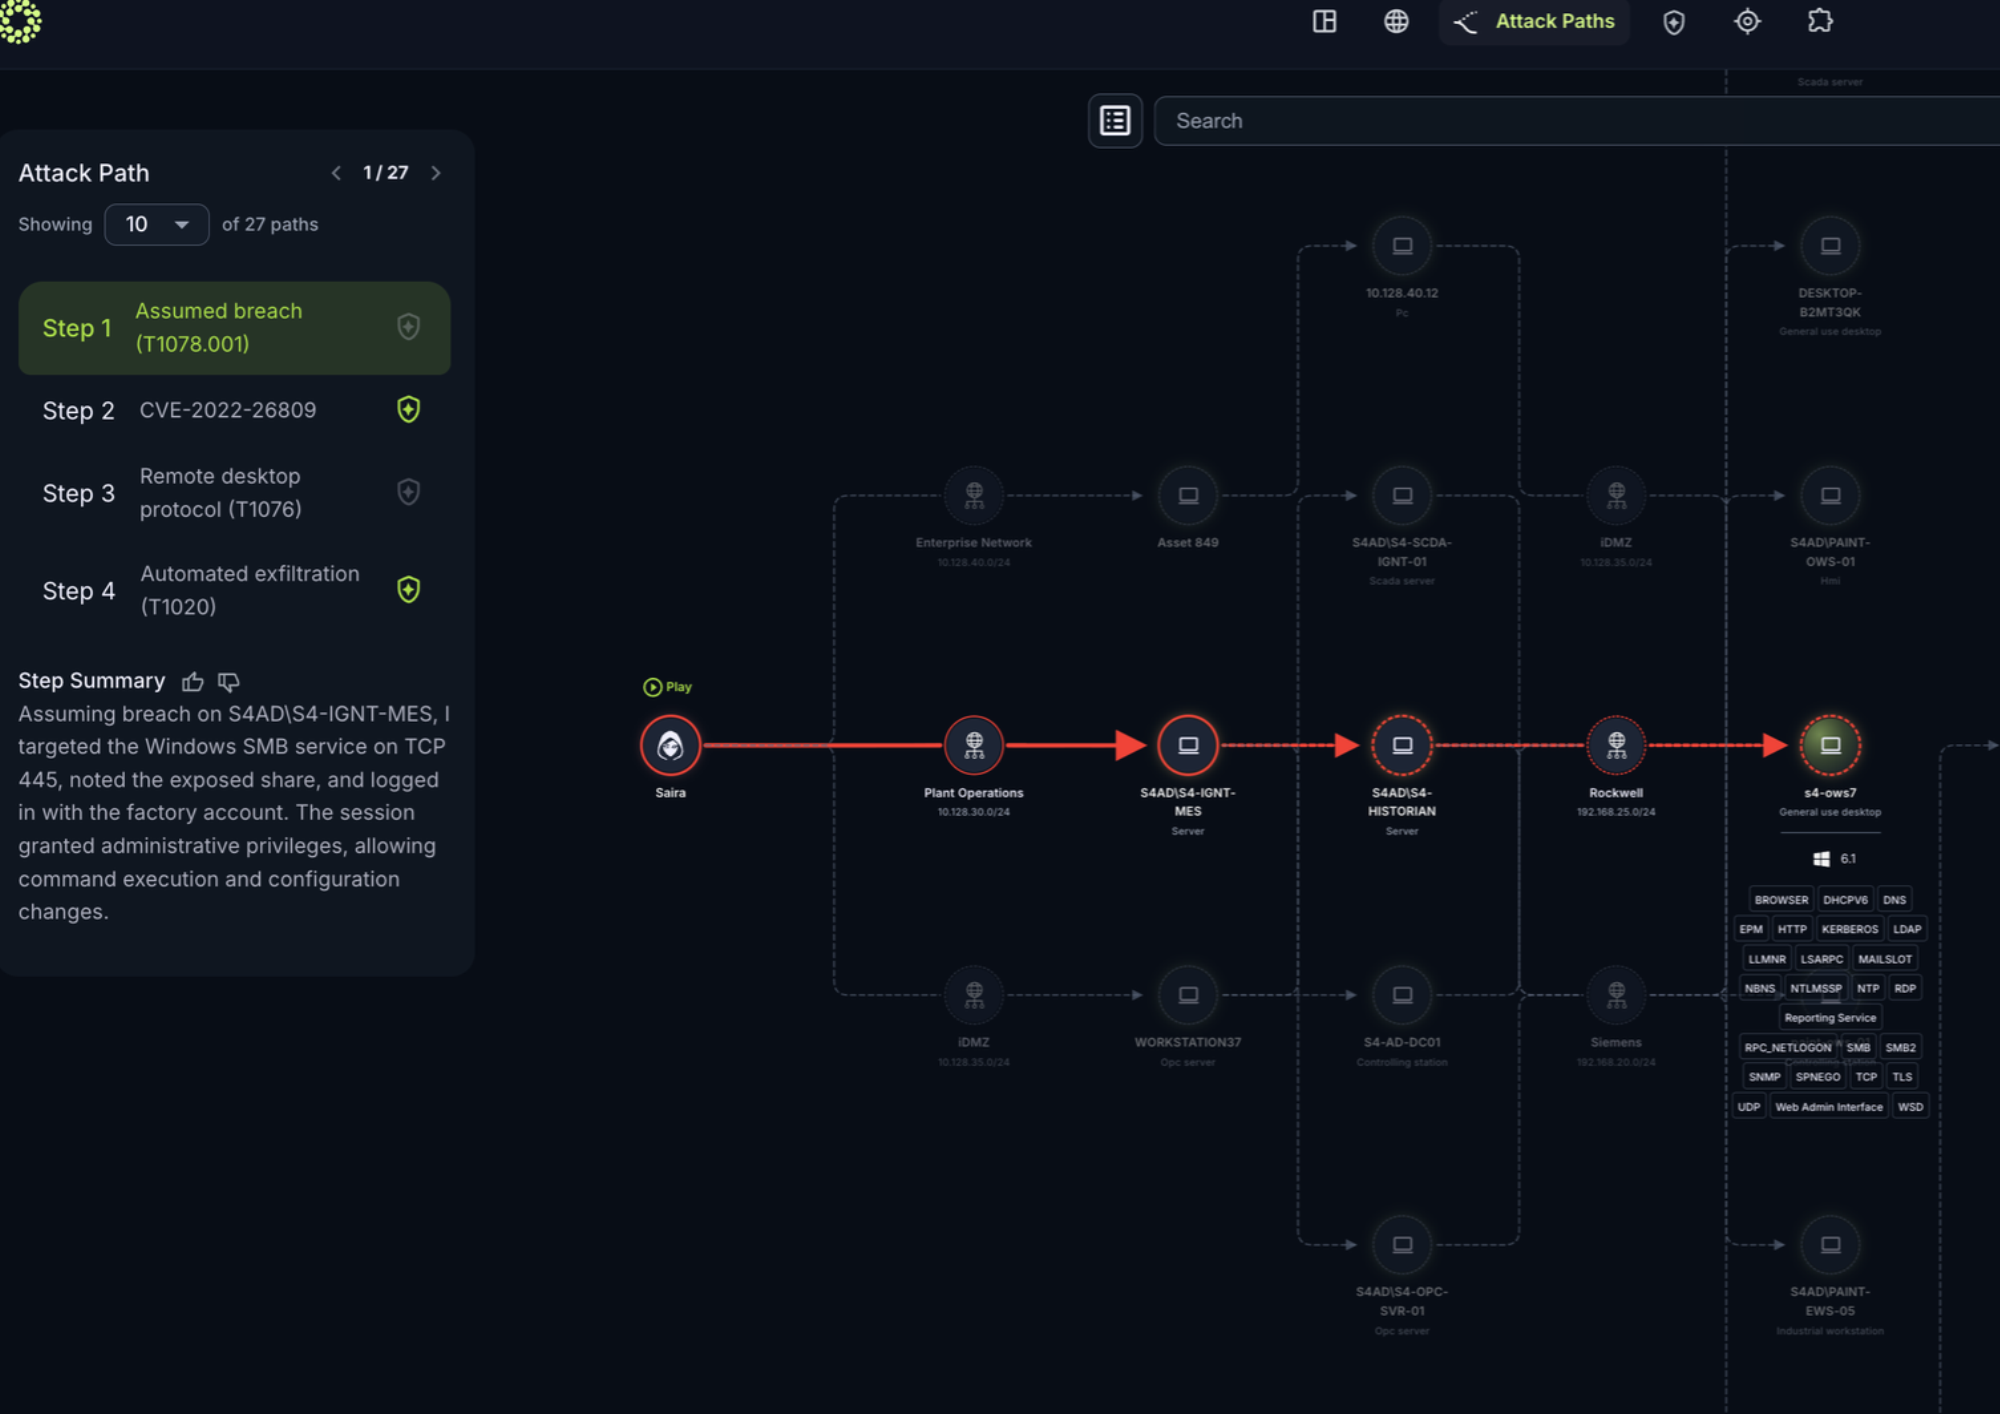
 

frenos attack path screenshot

We stay after the report

In Advisory and Implementation, we stay through the roadmap and re-validate after every change. When a path is not closed, we say so plainly. 
next steps
 

Get a clear view of your attack paths in just four days 

Four days on one site with more than two OT networks, built from data you already have, with no production access. Led by a TSG Managing Director working with Frenos. 
Digital twins blog post (3)